Contain faster.
Recover with confidence.
Preparedness, investigation and direct response for incidents where speed, evidence and clear decisions matter.
Bring structure to the moments that test your organization.
We help teams prepare before an incident, coordinate decisive containment during one and preserve the evidence needed for recovery, legal and regulatory obligations.
Incident response planning
Create a response program your team can execute under pressure. We define roles, escalation paths, communications, technical procedures and decision points around the incidents most relevant to your organization.
- Roles, escalation and communications
- Scenario specific response playbooks
- Tabletop exercises and lessons learned
24/7 incident support
Mobilize experienced responders when a serious event occurs. We rapidly scope impact, preserve evidence, coordinate containment and provide clear updates so leaders can make informed decisions throughout the incident.
- Rapid triage and investigation
- Containment and stakeholder coordination
- Executive situation reporting
Digital forensics
Preserve and analyze endpoint, identity, cloud and network evidence to reconstruct events and determine scope. Our work supports containment, recovery, legal review and defensible incident review reporting.
- Evidence preservation and chain of custody
- Timeline and root cause analysis
- Clear forensic findings and reporting
Ransomware & breach response
Coordinate the technical and operational response to ransomware, data exposure and complex intrusions. We help eradicate attacker access, restore trusted operations and manage the evidence required for stakeholders.
- Threat eradication and recovery support
- Compromise and data impact assessment
- Recovery hardening roadmap
Test the plan
before the crisis.
A written response plan is only useful when leaders and technical teams can execute it under pressure. Netreoun facilitates realistic, discussion based exercises that expose decision gaps, clarify accountability and improve coordination without disrupting production systems.
Practice a high pressure cyber event from detection through recovery.
Participants work through a realistic ransomware scenario involving compromised identities, encrypted systems, operational disruption and potential data exposure. The exercise tests containment authority, recovery priorities, communications, evidence preservation and decisions involving legal, insurance, regulators and customers.
Give business leaders the clarity to make difficult decisions quickly.
Executives rehearse their responsibilities during a material security incident. We focus on business impact, governance, disclosure obligations, stakeholder communications, risk acceptance and the information leaders need from technical teams to make defensible decisions.
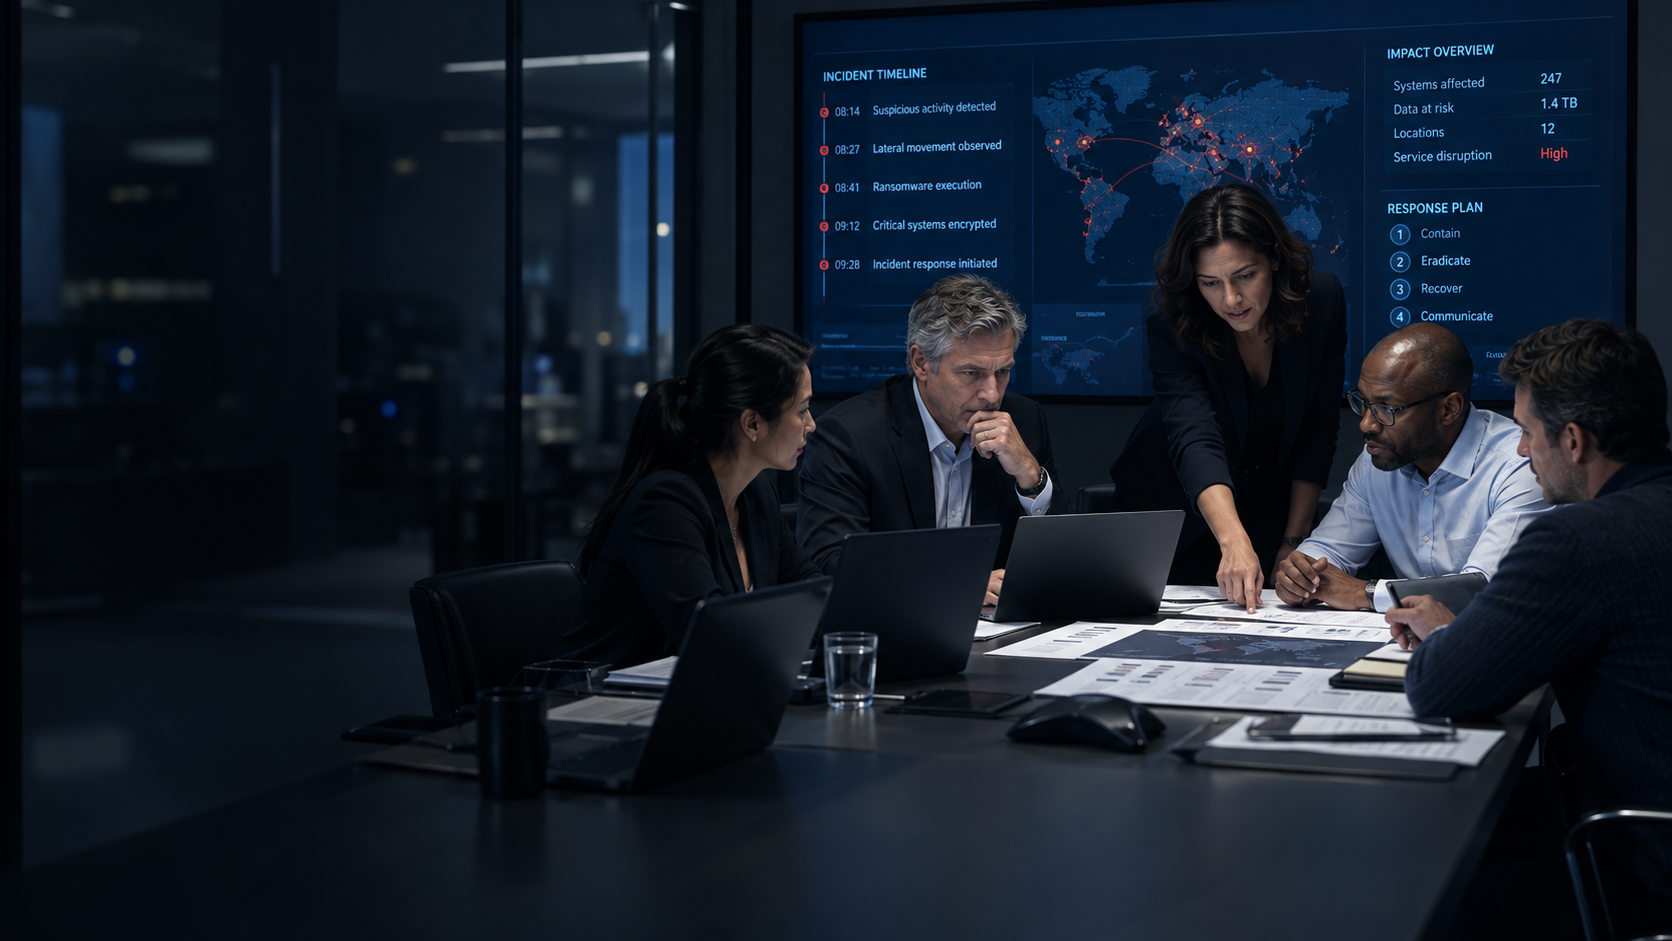
Practice the decisions before the pressure is real.
Ransomware simulations and executive tabletop exercises expose gaps in authority, communications, technical response and recovery while there is still time to improve.
Build stronger security operations.
Share your priorities, constraints and current control maturity. We will recommend the next practical step.